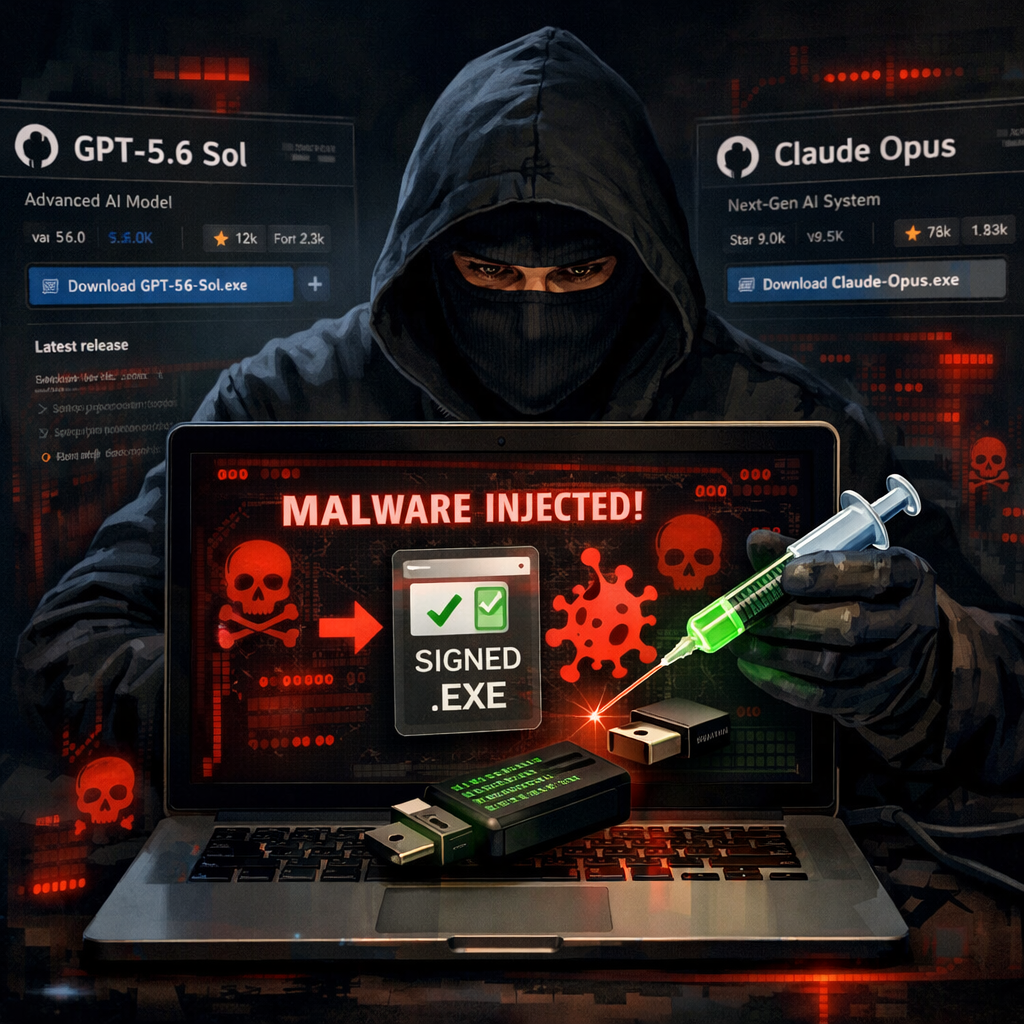
A newly discovered malware campaign, dubbed Yoba, is impersonating popular AI tools like ChatGPT and Claude to deliver malicious payloads disguised as legitimate software repositories. The attackers publish fake GitHub projects offering desktop apps with names such as GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. These look like real tools—complete with GitHub Pages sites and download buttons pointing to ZIP files in GitHub Releases—but they’re traps for unsuspecting users.
How the Attack Works
Check Point researchers found that the fake projects don’t fake stars or forks—often used to mimic popularity—but still manage to appear near the top of Google search results through “SEO poisoning,” manipulating metadata so search engines rank their pages high.
When a user downloads the ZIP and runs what appears to be a signed Setup.exe (from OpenAI or Anthropic), the malware activates a DLL-sideloading technique. A malicious winmm.dll accompanies the signed executable. Windows loads DLLs from the same directory as the application, letting the malicious component run under the guise of a legitimate process.
Behavior, Lateral Techniques, and Payloads
The installer—called YobaDropper—has anti-analysis checks. It verifies its filename (must be “Setup.exe”), confirms the system is not using Russian or certain post-Soviet keyboard language settings, and checks for administrator privileges. If it passes all checks, it copies a genuine Windows Media Player file into ProgramData, drops a component called YobaLoader, and schedules itself to run shortly after system boot—labelled as a Microsoft component to evade casual inspection.
YobaLoader doesn’t contact a fixed command-and-control server. Instead, it builds a domain name dynamically by fetching a Telegram channel’s profile image (from “yoba_fanclub”), extracting its last 50 bytes, and constructing a domain like adjective-noun-verb-number.dedyn.io. This design makes it harder for defenders to block domains. Commands are fetched via Google DNS-over-HTTPS using a TXT record (encrypted and signed), which then retrieves a payload from files.catbox.moe—current versions deliver an XMRig cryptocurrency miner routed through Tor. But the loader is generic, meaning future versions may download ransomware or data-theft tools.
Origins, Evolution, and Indicators of Compromise
The malicious commits in these projects use email addresses and timestamps spanning UTC+4, UTC-4, and UTC+3—likely to mask where the attackers really are. Compile timestamps align with UTC-4, and some forensic signals point toward Russian involvement, though nothing definitive has been proven. Earlier in 2026, Yoba’s operators used a component named Cursor.exe, showing the malware’s lures shift over time.
Protective Measures
Users should only download AI tools from official domains like openai.com or anthropic.com. Before running any software from GitHub, check the repository owner, account age, commit history, and contributor count.
Security teams should watch for signed executables loading DLLs from local folders, scheduled tasks labeled as Microsoft components, and abnormal DNS-over-HTTPS traffic. Also limit admin privileges and block unknown software sources. MITRE guidance suggests monitoring DLL loads and unexpected file activities.
Signs of compromise include setups that appear legitimate, dropper behavior aligned with pre-boot persistence, dynamically generated domains, and payloads delivered via signed and encrypted channels.
What It Means & What to Watch: This campaign highlights just how sophisticated AI-themed malware has become—blurring the lines between legitimate signed tools and stealthy threats. As attackers abuse digital trust with signed executables and domain obfuscation, both users and security teams need sharper defense strategies. Expect more mimicry attacks targeting high-profile AI names, and prepare for evolving payloads beyond cryptominers—ransomware or espionage tools could be next. Keep an eye on download sources and domain behavior; the future of malware is increasingly geared toward stealth, not brute force.