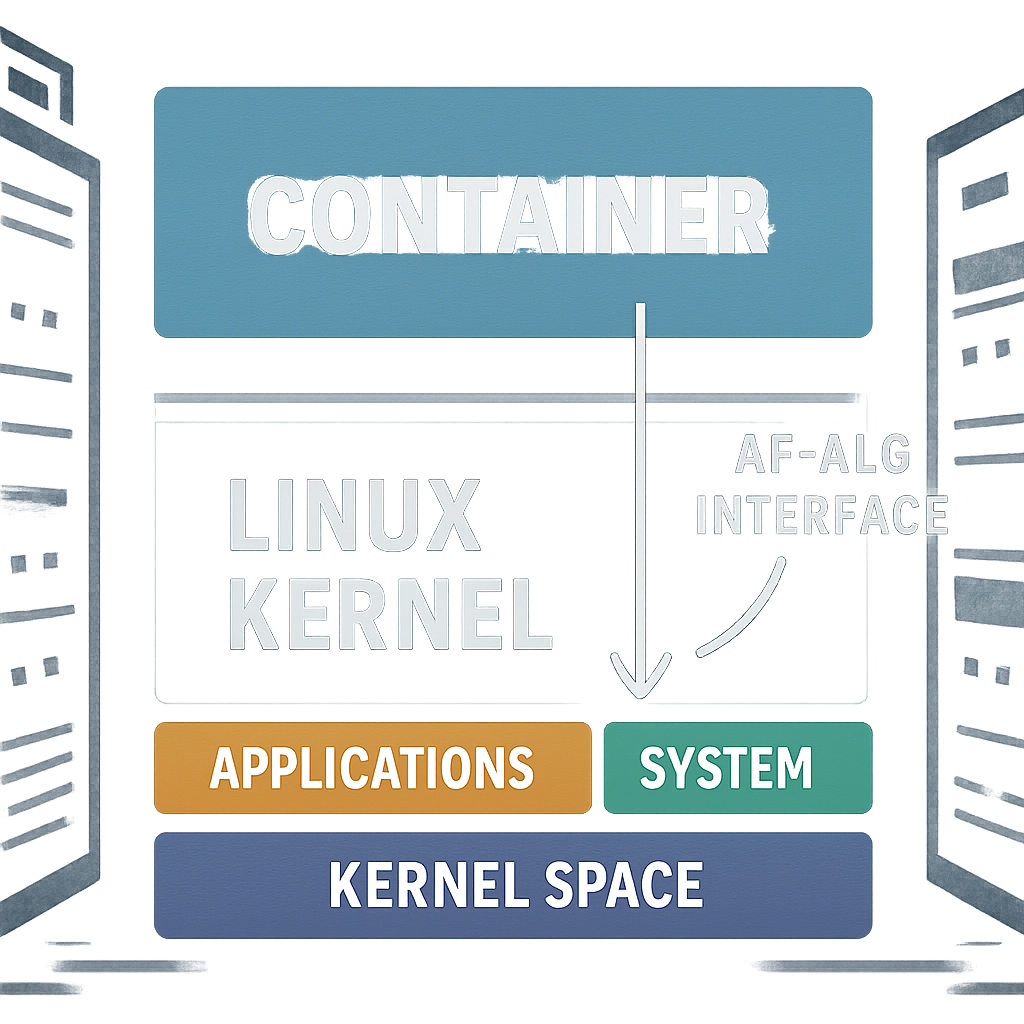
A critical vulnerability lurking in the Linux kernel for over a decade has been exposed, allowing a local attacker to elevate privileges to root and escape container boundaries. The flaw lives in the AF_ALG userspace cryptographic interface — commonly used for AES encryption and decryption — and arises from unsafe concurrent writes to the same socket. Because AF_ALG is accessible by unprivileged processes, this weakness offers a dangerous attack surface.
The Vulnerability & How It Works
The issue stems from a race condition in the AF_ALG sendmsg() path. In normal operation, Linux handles cryptographic input via buffers tracked with scatter-gather lists. A flag, “merge,” signals that the final buffer has unused space, allowing more data to be appended. However, when two threads write through the same AF_ALG socket, a race condition appears. While holding a socket lock, one thread may be paused waiting for writable buffer space. During that pause, another thread can change shared context, including that “merge” flag. If the merge flag remains enabled but the scatter-gather list has no valid entries, the result can be an out-of-bounds access — specifically an sg[-1] access into what should be protected metadata.
Attackers can exploit this to craft fake scatterlist entries under their control. This grants them a usercopy oracle scenario, which they can escalate into an arbitrary kernel write. From there, the exploit targets the kernel’s core_pattern setting — a string that determines how Linux handles core dumps. Because core_pattern can invoke a pipe, altering it lets an attacker force a dumped process to execute their own binary with root privileges. In containerized environments (such as Docker), that means escaping from inside a container into the host system.
Discoverer, Exposure, and Fixes
Researcher Muhammad Alifa Ramdhan of STAR Labs identified the bug in 2025 during a code audit for Google’s kernelCTF program; a colleague, Bing-Jhong Billy Jheng, also contributed. Their work demonstrated a stable, reliable exploit path from local unprivileged user to root access. The research earned a reward of $113,337. The issue has been assigned CVE-2025-39964 and is officially recognized by CISA as being exploited in the wild.
This vulnerability was introduced with Linux kernel version 2.6.38 back in 2011 and persisted—sometimes due to backported kernels—until patches were released. Fixed versions include at least Linux 5.10.246, 5.15.195, 6.1.155, 6.6.109, 6.12.50, and 6.16.10. The corrective change enforces exclusive write ownership for AF_ALG contexts: if a second writer attempts to act while a context is already being written, the operation fails instead of corrupting shared state.
Mitigation & Urgency
To protect systems, administrators should patch affected kernels immediately and reboot into updated versions. This is especially crucial for environments with shared infrastructure like container hosts, multi-user systems, or those where untrusted local code can run. Since containers share the host kernel, this bug means that a compromised container could lead directly to compromising the host.
This long-standing flaw underscores that even old kernel code can hide serious vulnerabilities. It’s a reminder that rigorous auditing, especially in cryptographic and shared resource modules, remains essential. Moving forward, eyes will be on how distributers manage backports, how many systems remain vulnerable, and whether attackers create public exploits now that the technical details are out. The speed and breadth of patch adoption will determine if this becomes another remote disaster or a contained, teachable moment for Linux security.