A new ad-based campaign has been uncovered that delivers counterfeit security warnings, locking down browsers and attempting to install malware. The deceptive scheme begins with Google Ads directing users to what looks like normal online stores, only to escalate into full-blown system scare tactics.
How the Scam Unfolds
Protective researchers at Netskope discovered a scam kit that operates through paid ads and cloud-hosted landing pages. At first glance, users see a routine storefront interface or a benign splash page. The real menace appears only after human interaction, when the page insists something is wrong with the visitor’s Windows or Mac system.
The toolkit includes several evasive features: ads are served across widely used sites — weather, sports, map services — without the sites themselves being compromised. The malicious content hides behind code that decrypts only when specific cues like mouse movements are detected, avoiding automated detection tools.
The Alert Tactics
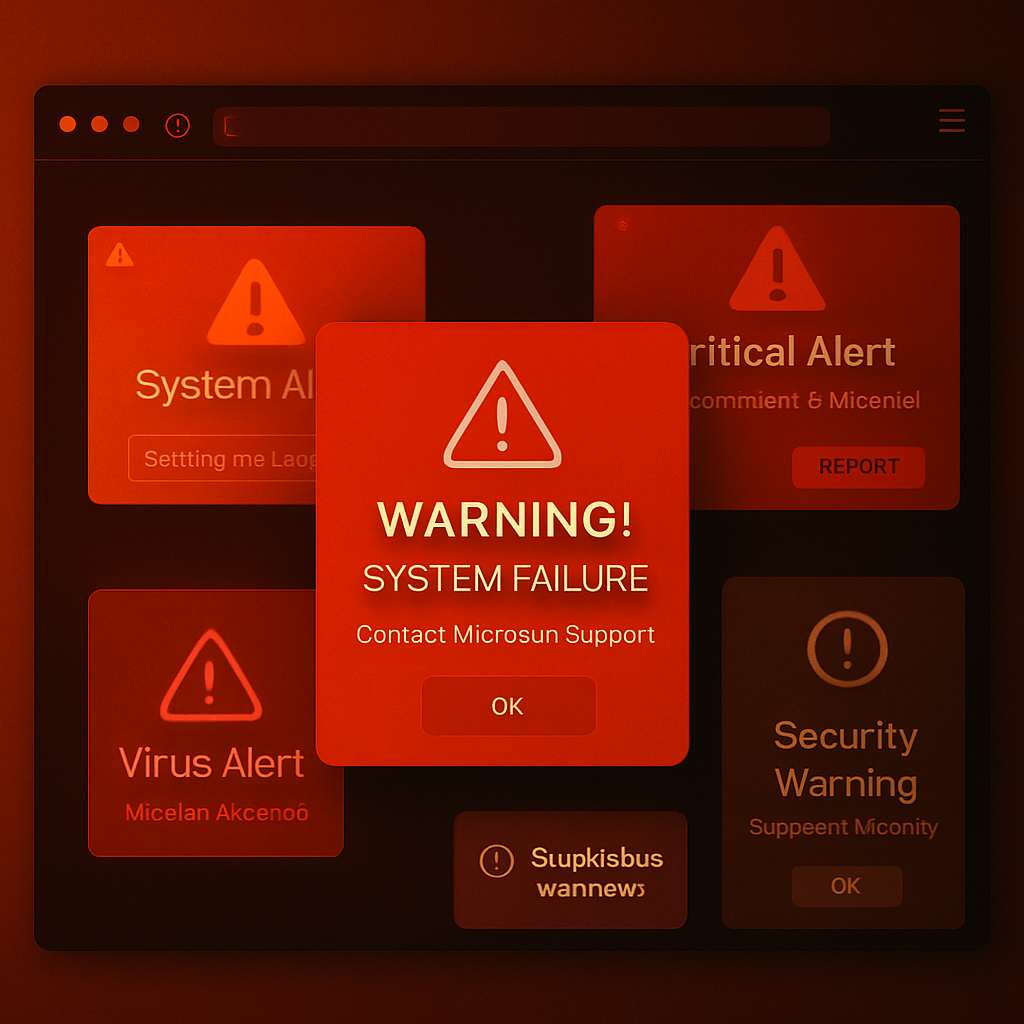
Once triggered, the script simulates alarming system alerts. On Windows machines, it mimics Microsoft Defender scan results. For Macs, it poses as Apple-style notifications. Both versions pepper the screen with warnings, insist a support phone number be called, and attempt to trap users by blocking normal browser controls — hiding the address bar, altering cursor behavior, even suppressing tab closing. However, none of this involves actual malware installation at that stage — it’s all show.
Scope and Targets
The campaign was active between August 31 and September 14, 2026. During that period, at least 619 organizations across 284 legitimate websites were targeted through over 250 distinct ad campaigns, and at least 457 scam-linked hosts were identified. The majority of affected entities were in the U.S., with Japan and Australia also notably impacted.
Preventing the Trap
Experts advise users to avoid calling any number provided in such alerts. If a browser session forces full-screen or locks down interface controls, holding down the Escape key or force-quitting the browser (or using Task Manager on Windows) can help exit the experience. The critical thing is not to provide personal or financial information on these pages.
This incident builds on a long-standing trend: the rise of digital scareware campaigns that use plausible-looking warnings to deceive and intimidate. Even with benign first impressions—like a cloud-hosted storefront — the goal is always escalation.
What this means: paid ad networks remain a dangerous vector for social engineering. The blending of legitimate domain reputations, invisible triggers, and browser hijacking shows how threat actors continue to be creative. Watch for fake alerts, especially after clicking ads on even well-known sites. For businesses, scanning ad partners and auditing inbound traffic can help. For individuals, skepticism when a site insists something is critically wrong — especially with pressure to call a number — could be your first line of defense.