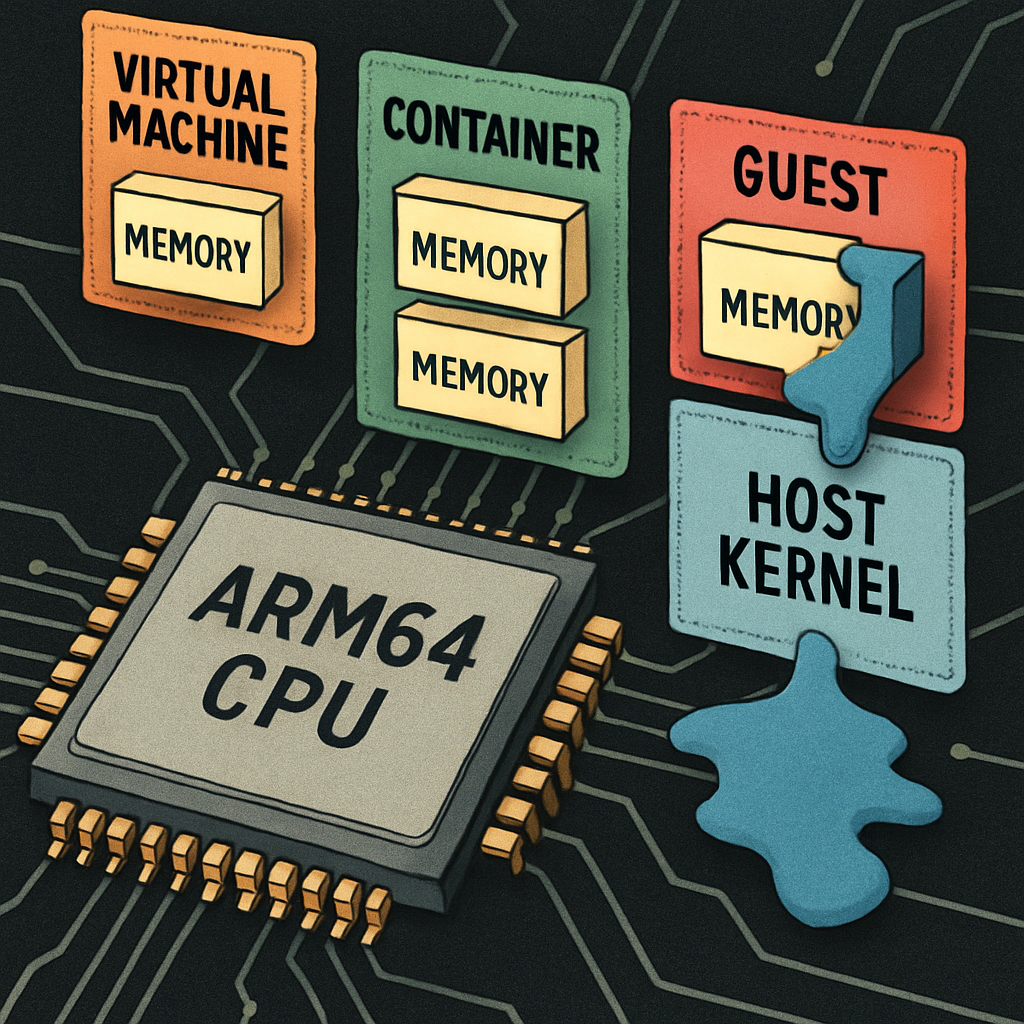
Linux systems using KVM virtualization on ARM64 processors face a severe vulnerability, tracked as CVE-2026-89775, that enables guest virtual machines to gain read-write access to the host’s kernel memory. The flaw, specific to ARM64 nested virtualization setups, can allow a guest VM to escape its sandbox and execute code on the host machine. The issue was disclosed on September 16, 2026, by security researcher Hyunwoo Kim.
How the Flaw Works
The vulnerability impacts the component of the Linux kernel that handles nested virtualization on ARM64. In certain memory layouts crafted by a guest, a size calculation erroneously returns zero, causing a critical step—clearing stale translations in the processor’s translation lookaside buffer (TLB)—to be skipped. As a result, a page of host memory that has been freed remains mapped and writable from the guest, allowing read/write access without triggering a hardware trap.
This attack path requires nested virtualization to be enabled, which is off by default. ARM64 nested virtualization is an experimental mode at boot time, requiring Armv8.4 hardware with the FEAT_NV2 feature enabled. Hosts without this configuration are not vulnerable along this vector.
Who’s Affected & What’s Already Patch
The issue is present in the mainline Linux kernel starting around version 6.16. However, the behavior that allows exploitation only starts appearing from kernel version 6.17 onward. Versions 6.18.51, 7.2.5, and the 7.3-rc1 release include a full patch.
Major distributions differ in exposure: Red Hat Enterprise Linux’s Version 10 kernel is affected, while Versions 6–9 are not. Ubuntu 26.04, including its cloud kernels from AWS, Azure, and GCP, is vulnerable. Ubuntu 24.04’s core general kernel is not, though newer hardware-enablement kernels in that branch may be. Amazon Linux AL2023’s 6.18 kernel package is pending a fix, while its other kernels remain unaffected. In Debian, bookworm and trixie are clean, sid has been fixed in version 7.2.6-1, but forky remains vulnerable.
Exploit Scenarios, Risk & Mitigations
If this flaw is leveraged, guests could execute code at the host privilege level, a significant breach of isolation. One vector involves guests escaping confinement; another could let local users who can open /dev/kvmgain full root access. This second path is relevant in Red Hat’s default configurations.
Since nested virtualization is not enabled by default on ARM64 systems, many installations are safe unless explicitly configured otherwise. Disabling nested virtualization or ensuring that kernels are updated to corrected versions are the primary mitigations. No vendor offers a fully sufficient workaround once nested virtualization is turned on.
Impact for Cloud Providers & Threat Assessment
Cloud tenants might worry the flaw could let them jump from guest instances to host infrastructure. But large providers seem largely unexposed to this path. For example, AWS lists nested virtualization only for Intel-based instances, and Google Cloud excludes ARM VMs from its nested virtualization feature.
The flaw has received high severity scores from vendors—between 7.8 and 9.3 out of 10. However, exploit code has not surfaced in the wild, and it is not listed in the U.S. CISA catalog of exploited vulnerabilities. Predictions place its likelihood of exploitation in most cases as below 1%.
CVE-2026-89775 marks the fourth guest-to-host KVM escape disclosed this year. Previous escapes include two x86 KVM vulnerabilities and one ARM64 escape named ITScape in June. This pattern highlights ongoing risks in virtualization security across architectures.
Bottom line:systems with ARM64 architecture that have nested virtualization enabled and run vulnerable kernel versions must update immediately. Those without nested virtualization enabled are less exposed but should still monitor updates closely.
This flaw underscores the fragility of guest-host isolation in virtualized environments—especially when nested virtualization is involved. As cloud providers and enterprises push more work onto ARM64 infrastructure, rigorous auditing of virtualization code becomes critical. Watch for how major distributions perform remediation and whether any public exploits emerge. If you’re responsible for security in ARM-based deployments, ensure kernel updates and disable nested virtualization unless absolutely needed.