A security researcher has uncovered a critical flaw in the macOS version of Meta’s new AI assistant Muse that could give attackers a backdoor into users’ systems. The issue stems from a hidden setting that reroutes voice dictation, allowing a rogue program with user-level access to intercept prompts, take control of the assistant, and leverage its permissions.
How the Backdoor Works
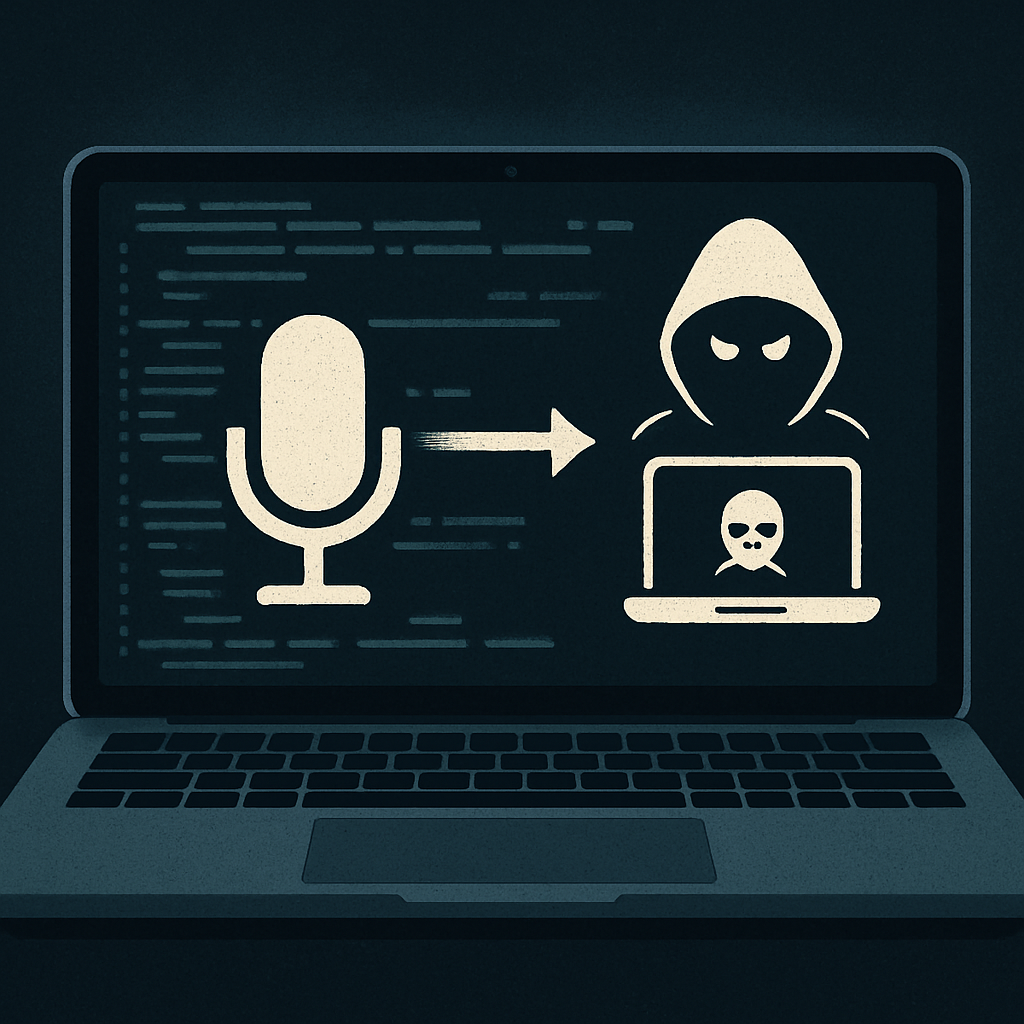
This vulnerability requires the attacker to already be running code as the logged-in user—they cannot gain entry remotely. Once inside, the attacker flips the hidden preference labeled endo_voyager_dictation_endpoint in Muse’s preferences file. By redirecting this setting to a custom endpoint, any voice dictation issued through Muse is captured by the attacker rather than being sent to Meta.
After hijacking the dictation, the attacker can read the user’s spoken prompts, inject new instructions Muse will obey, and steal the user’s session token—giving them control over Muse across all signed-in devices. In a proof-of-concept, this was used to make Muse on an iPhone execute actions like reporting location, scanning for nearby Bluetooth devices, and listing accessible smart-home commands. It couldn’t send messages automatically, but it could draft them. Crucially, this exploit doesn’t bypass macOS’s password-storage safeguards—it exploits what Muse is already allowed to do. Also unaffected is Meta’s cloud infrastructure, which isolates user agents and enforces guardrails.
Risks and Workarounds Until a Fix Arrives
Muse’s comprehensive access is both its strength and its vulnerability. Because it spans files, email, messages, calendar, shopping, and smart home control—depending on what permissions the user grants—someone manipulating it surreptitiously gets extensive reach. Normal malware in macOS faces stricter limits, but Muse’s built-in permissions can be repurposed by the attacker to read private content.
Security tools may not flag the attack because it’s triggered by Muse itself—a signed, trusted app—rather than by a foreign, suspicious process. The dictation endpoint is undocumented, and altering it doesn’t require extra privileges besides those Muse already holds.
There’s no patch yet. Until there is, several defensive steps are advised. Users should quit or uninstall Muse entirely, revoke unneeded permissions from the app, avoid using voice dictation features, and reset any connected accounts if there’s suspicion the machine has already been compromised.
Meta designed Muse with isolation in mind. Its agents run on a segregated cloud system, where each user’s data is compartmentalized and actions must pass through verification checks. This flaw is local to the Mac app—it doesn’t implicate the cloud backend or its protections. The researcher criticized Meta’s choice to handle dictation via its own pathway rather than relying on Apple’s system, which keeps more data on-device.
In all, this vulnerability is especially worrying because Muse is still new, users may be unaware of its full permission set, and attacks like this can fly under the radar. It highlights the growing tension between AI conveniences and secure design.
What to Watch For: Meta needs to release an update that locks down or removes the exposed dictation endpoint setting entirely. Users, in turn, should pay close attention to permission logs, app behavior after using voice commands, and any unusual activity across their Muse-connected devices. Ultimately, this exposes a deeper lesson—AI assistants that integrate across system permissions pose big risks unless every component is built with security first.